
The single most important rule: generate a unique passphrase for every gated asset, then split its delivery so the link and the password never travel through the same channel. Add a short lifespan or click cap wherever the content allows it, since stale credentials are the ones that leak. Some platforms build password protection, expiration settings, and click analytics directly into their link hubs, so this workflow can take minutes instead of a spreadsheet of workarounds.
TL;DR:
- Reusing passwords across gated assets significantly increases the risk of widespread leaks, so each link requires a unique passphrase.
- Deliver the link and password through separate channels to prevent interception of both, especially avoiding public comments or open messages.
- Set expiration dates and click limits aligned with the content’s relevance to reduce leak windows and monitor for suspicious activity.
- Rotate passwords regularly for long-term assets and move to member-specific access as the audience expands beyond a few hundred.
- Use link hubs that support password protection, expiration, and analytics to automate security and quickly respond to any signs of leaks.
Table of Contents
- What Are the Best Practices for Password-Protected Links?
- How Do You Split Delivery Across Channels?
- When Should You Rotate or Expire a Password?
- Should You Gate or Preview Your Content?
- What Should You Monitor After Sharing a Password?
- How Does Lflow Support Secure Link Sharing?
- Why This Matters More as Your Audience Grows
- Ready to Put These Practices to Work?
- Sources
- FAQ
What Are the Best Practices for Password-Protected Links?
Before you paste a single protected link into your bio, run through this checklist. It takes less time than writing the caption.
- Generate a unique passphrase per asset. Reusing "vip2026" across every gated drop means one leak compromises everything you've ever protected.
- Never send the link and password together. Pairing them in the same DM, email, or caption defeats the entire point of gating, since anyone who intercepts one message gets both halves at once, according to guidance on password-protecting short links.
- Split delivery across two channels. Put the link where your audience already expects content and send the password somewhere more private.
- Set an expiration or click limit on anything time-sensitive. A password for a 48-hour replay shouldn't still work in June.
- Rotate credentials on long-lived assets. If a resource stays live for months, refresh the password on a schedule rather than never.
- Reserve gating for private or paid content, not marketing pages. A password wall on a page you want Google to index kills your own discoverability.
- Use HTTPS destinations and watch your analytics for odd spikes. Traffic patterns tell you when something's wrong before a subscriber does.
Pro Tip: Keep a simple log (even a private note) of which password went to which cohort and when. When something leaks, that log tells you exactly which distribution list to investigate first.
How Do You Split Delivery Across Channels?
Channel splitting means the link lives in one place and the password lives somewhere else entirely, so a leak in one location doesn't hand over full access. Someone who screenshots your public post still needs to find the password, and someone who forwards a DM still needs the link. It's a low-effort trade that meaningfully raises the bar for casual leakers, since intercepting both halves at once requires monitoring two separate channels, not one.
Here's how that plays out in practice:
- Paid subscribers: Create the branded link, enable the password, post the link in your subscriber-only feed or bio, then text or email the password directly to paying members.
- Event attendees: Generate the link and password, print or project the link as a QR code at check-in, and hand out the password verbally or on a printed card.
- Collaborators: Share the link in a shared drive or project channel, then send the password through a direct message or a quick call.
The mistake almost everyone makes at some point: posting the password in a public comment reply "just this once." One slip-up in a public thread erases every precaution you took setting it up.
When Should You Rotate or Expire a Password?
Passwords protecting active content shouldn't live forever. The longer a credential stays valid, the more inboxes, screenshots, and forwarded messages it ends up sitting in, and every one of those is a potential leak point you can't monitor. Building expiration and click limits into your gating habit shrinks that exposure window automatically instead of relying on memory.
A few operational rules that work well in practice:
- Match the expiration to the content's shelf life. A 24-hour flash sale gets a 24 to 48 hour password; a permanent resource library gets a quarterly rotation instead.
- Set click limits on anything meant for a small, known group. If you're sharing with 40 people, a cap slightly above that number flags unusual activity fast.
- Notify legitimate users before rotating, not after. A quick "new password drops Monday" message avoids a wave of confused support requests.
- Move to named access once your list outgrows casual sharing. Somewhere around a few hundred recipients, an email whitelist or a membership platform becomes easier to manage than a single shared password, and it protects your revenue better as the audience compounds.
- Reissue promptly and transparently when you do rotate. Paying members forgive a password change; they don't forgive being locked out with no explanation.
Should You Gate or Preview Your Content?
A hard paywall protects everything but converts almost nobody, since visitors can't evaluate what they're paying for before they commit. A preview-and-gate model, where you show a teaser and lock the rest, tends to perform better because it lets discovery happen in public while the valuable part stays protected. Hybrid setups that combine open previews with gated depth typically outperform an all-or-nothing wall, according to membership gating strategy research.
Where each approach fits:
- Use previews and teasers for paid tutorials, template packs, or replays. Blur the thumbnail, show the first section free, and gate the payoff.
- Skip gating entirely on SEO pages, public marketing content, and QR codes meant for cold traffic. A password wall there just blocks the audience you're trying to grow.
- Use gating to signal exclusivity, not to hide mediocre content. A protected drop should feel like a reward for subscribing, not a paywall slapped on filler.
What Should You Monitor After Sharing a Password?
Your analytics dashboard is the first place a leak shows up, usually before anyone emails you about it. Watch for a sudden spike in clicks that doesn't match your subscriber count, traffic from geographic regions your audience doesn't live in, repeated hits from a single IP range, or referrers you never sent the link to.
If you spot one of those signals, move fast:
- Rotate the password immediately and revoke or expire the old link.
- Notify your legitimate audience with the new credential and a short, honest explanation.
- Trace the leak by checking your recent sends for who received that specific password.
- Tighten future delivery by splitting channels more aggressively or moving high-value content to per-user access instead of a shared password.
Pro Tip: Set an automatic redirect to a "link closed" page once a password expires or hits its click cap. It stops confused clicks cold and gives you a clean moment to reissue access on your terms.
Worth remembering: a password gate controls who gets in, but it doesn't stop someone who's already inside from screenshotting or re-sharing what they find. Treat it as a filter for casual access, not a lock against a determined leaker.
How Does Lflow Support Secure Link Sharing?
Certain link hub services support workflows with password protection, expiration settings, and click limits on every gated link, alongside real-time analytics that flag spikes and odd referrers. QR codes can generate automatically for offline distribution at events or in print materials.
A typical setup looks like this:
- Create a branded short link for the asset you're gating.
- Turn on password protection and set a passphrase unique to that drop.
- Add an expiration date or click cap based on how long the content stays relevant.
- Distribute the link through your bio and send the password through a separate, private channel.
- Watch the analytics dashboard for unusual activity, then rotate or revoke as needed.
That loop, repeated for every gated asset, turns a manual security habit into something closer to routine maintenance.
Why This Matters More as Your Audience Grows
Password gating is a professional boundary, not a technicality. It tells your audience that access to certain content is earned, not scraped off a public feed. Start with the basics: split your delivery channels and set expirations on anything time-sensitive. As your list grows past a few hundred, graduate to membership or email-whitelist access instead of stretching one shared password further than it should go. Judge success by engagement and conversion, not just by counting leaks you never had.
— Axion
Ready to Put These Practices to Work?
Some platforms offer password protection, expiration dates, click limits, and real-time analytics on each link in a hub, making the setup feasible with just a few clicks instead of workarounds.
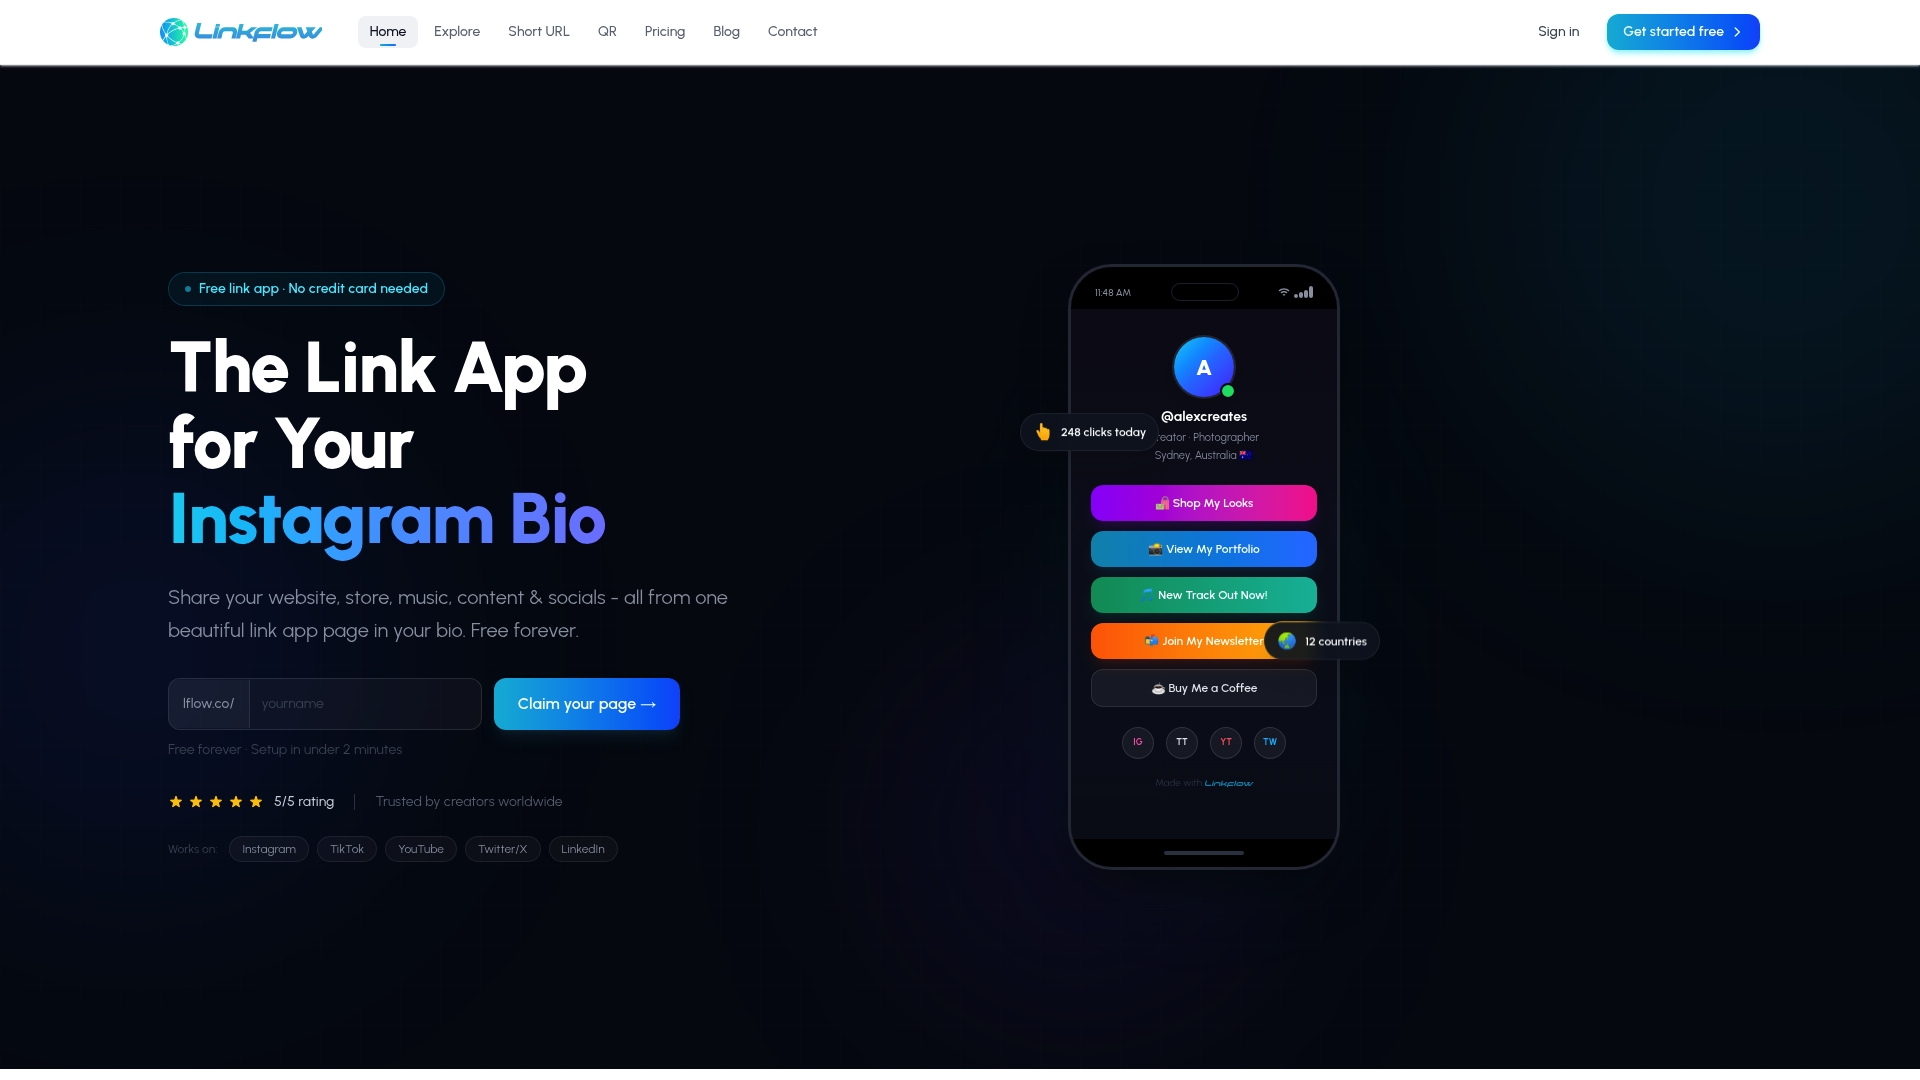
If you're setting up your first gated drop, start with the free link in bio page, which includes unlimited links and QR codes at no cost. Pair a protected link with a QR code for in-person events, where handing out a password verbally works better than posting it anywhere public. Once your gated content library grows, the paid plans add custom domains and deeper analytics for tracking exactly who's clicking what. Set up your hub now and gate your next drop the right way from the start.
Sources
For deeper implementation detail, see the complete guide to password-protecting short links, the creator-focused breakdown of gated bonus links, and the practical guide to membership gating strategy. Creators managing gated hubs at scale should also review gated content hub monetization and, for those hosting on Webflow, the Webflow security plugin roundup.
FAQ
Is a password-protected link the same as encryption?
No. Password protection controls who can access the link, but it doesn't stop someone who already has access from re-sharing the content itself.
How often should I rotate a password on gated content?
Match rotation to the content's shelf life: short-term drops get a new password every 24 to 48 hours, while permanent resources can rotate quarterly.
Where should I send the password if not in the same message as the link?
Use a separate private channel like a DM, paid newsletter, or in-app message, since sending both through the same channel defeats the protection entirely.
Can Lflow set expiration dates and click limits on protected links?
Yes, Lflow supports password protection alongside expiration settings and click limits on the same link, with real-time analytics to monitor activity.
Should I ever put a password-protected link in a public post?
No. Posting a protected link publicly invites brute-force attempts and hurts conversion, since it signals a wall before visitors know what's behind it.